
Why moving looks like an attack
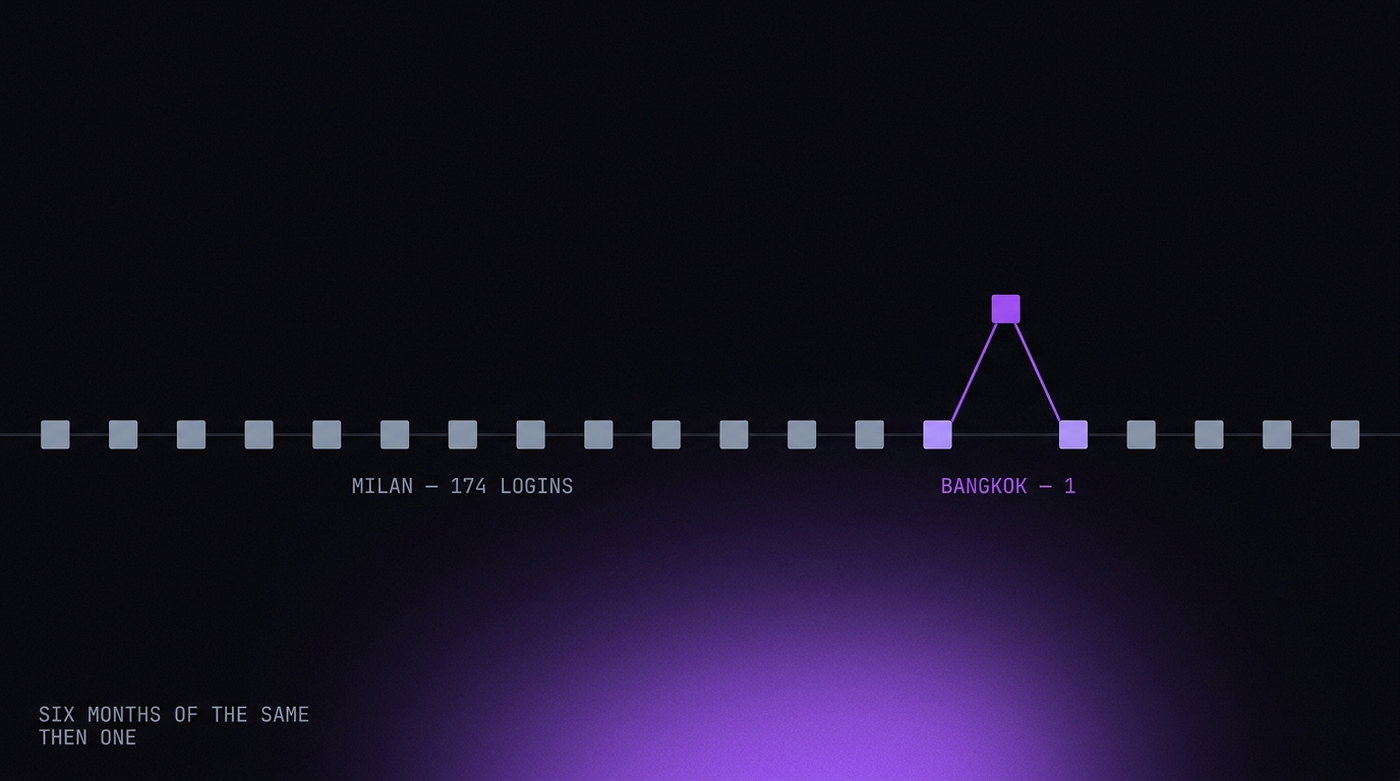
Login systems are built to spot one thing above all others: a session appearing somewhere it could not plausibly have travelled to. The industry name is impossible travel, and the logic is simple — you logged in from Milan at 09:00 and from São Paulo at 11:00, and no aircraft covers that.
Real travel is not impossible, but it does trip nearly every other check at once. In a single moment you change your IP address, your country, your internet provider, your timezone, and often your language settings and your network type. That is five or six simultaneous changes to an account whose history says none of them ever change.
Nothing has gone wrong. You have simply produced the same pattern as someone who stole your session, and the system cannot tell the difference from the data alone.
What actually gets checked
Roughly in order of how much weight each carries.
- Distance and time between logins. The impossible-travel calculation. A flight is fine; teleportation is not — which is why a VPN switched on mid-trip is worse than the trip itself.
- Network reputation. Hotel and airport wifi are shared by thousands of strangers, and some of those strangers have behaved badly from the same address. Café wifi is worse.
- Timezone against IP. If your laptop clock still says Rome while your address says Bangkok, that mismatch is checked directly and it is easy to spot.
- Device recognition. The one thing working in your favour. If the browser looks like the same machine as always, that counts for a lot — which is why travelling with your own laptop is far smoother than borrowing one.
- What you do next. Logging in and reading is normal. Logging in and immediately changing a password, adding a payout method or launching spend is the pattern of a takeover.
Before you go
Twenty minutes of preparation prevents most of it.
- Check your recovery options now. The worst version of this is being locked out abroad because the verification code goes to a phone number that does not roam. Confirm your recovery email works and that you can receive codes on the number you are travelling with.
- Turn on an authenticator app for anything important. App-based codes work offline and do not depend on your carrier. This one change fixes the most common travel lockout.
- Save backup codes offline. Printed, or in a password manager you can reach from a phone.
- Log in from home the day before. A recent successful session from your usual place gives the system a clean reference point.
- Do not change anything else that week. New password plus new country plus new device is three signals at once.
While you are there
The habits matter more than any setting.
Use your own connection where you can. Phone tethering beats hotel wifi comfortably — a mobile carrier address is shared with ordinary people doing ordinary things, and a hotel network is shared with whoever else is in the building.
Set your laptop clock to local time. Automatic timezone handles this if you let it. Leaving it on your home timezone creates a mismatch that costs you nothing to avoid.
Be boring for the first day. Log in, read, close it. Do the account maintenance later in the trip, once there is a small history from the new location.
Do not switch a VPN on and off. Appearing in three countries in one afternoon is worse than appearing in one new one and staying there. If you use a VPN abroad, pick one exit and keep it.
Expect one verification and treat it calmly. A code request after landing is the system working as intended. Complete it properly. Do not respond by changing your password, which turns a routine check into a suspected compromise.
Accounts that should not travel at all
Some accounts are worse than others at handling a move, and it is usually the ones you can least afford to lose.
Advertising accounts, marketplace seller accounts, payment accounts and anything tied to a business entity are all evaluated against a location history, and a sudden change of country can trigger a review that outlasts your trip. A verification you can clear from home in two minutes becomes a week-long problem from a hotel room.
For those, the better answer is to not move them at all. If the account has always operated from one place, it should keep operating from that place while you are away — which means the account's connection stays put even though you did not.
This is one of the more mundane reasons people end up with per-profile proxies: not to hide anything, but so that a business account does not change country every time its owner takes a holiday. The profile keeps its address, its timezone and its language wherever the laptop happens to be, and from the platform's side nothing happened at all.
If you are locked out anyway
It happens. The order of operations matters.
- Try from the same connection you first triggered it on. Switching networks mid-recovery adds another change to a system already unsure about you.
- Use the recovery method you set up before leaving, not a new one. Adding a new recovery route during a lockout is the pattern of an account takeover.
- If it needs a phone code and your number does not roam, this is where the backup codes earn their keep.
- Wait it out where possible. Many travel-triggered restrictions are time-limited and clear on their own. Repeated attempts extend them.
- If it becomes a real restriction, the general guidance applies — one careful appeal, and none of the three mistakes.
And the thing worth internalising for next time: the trip is not the problem. The problem is that your account had no idea it was coming.